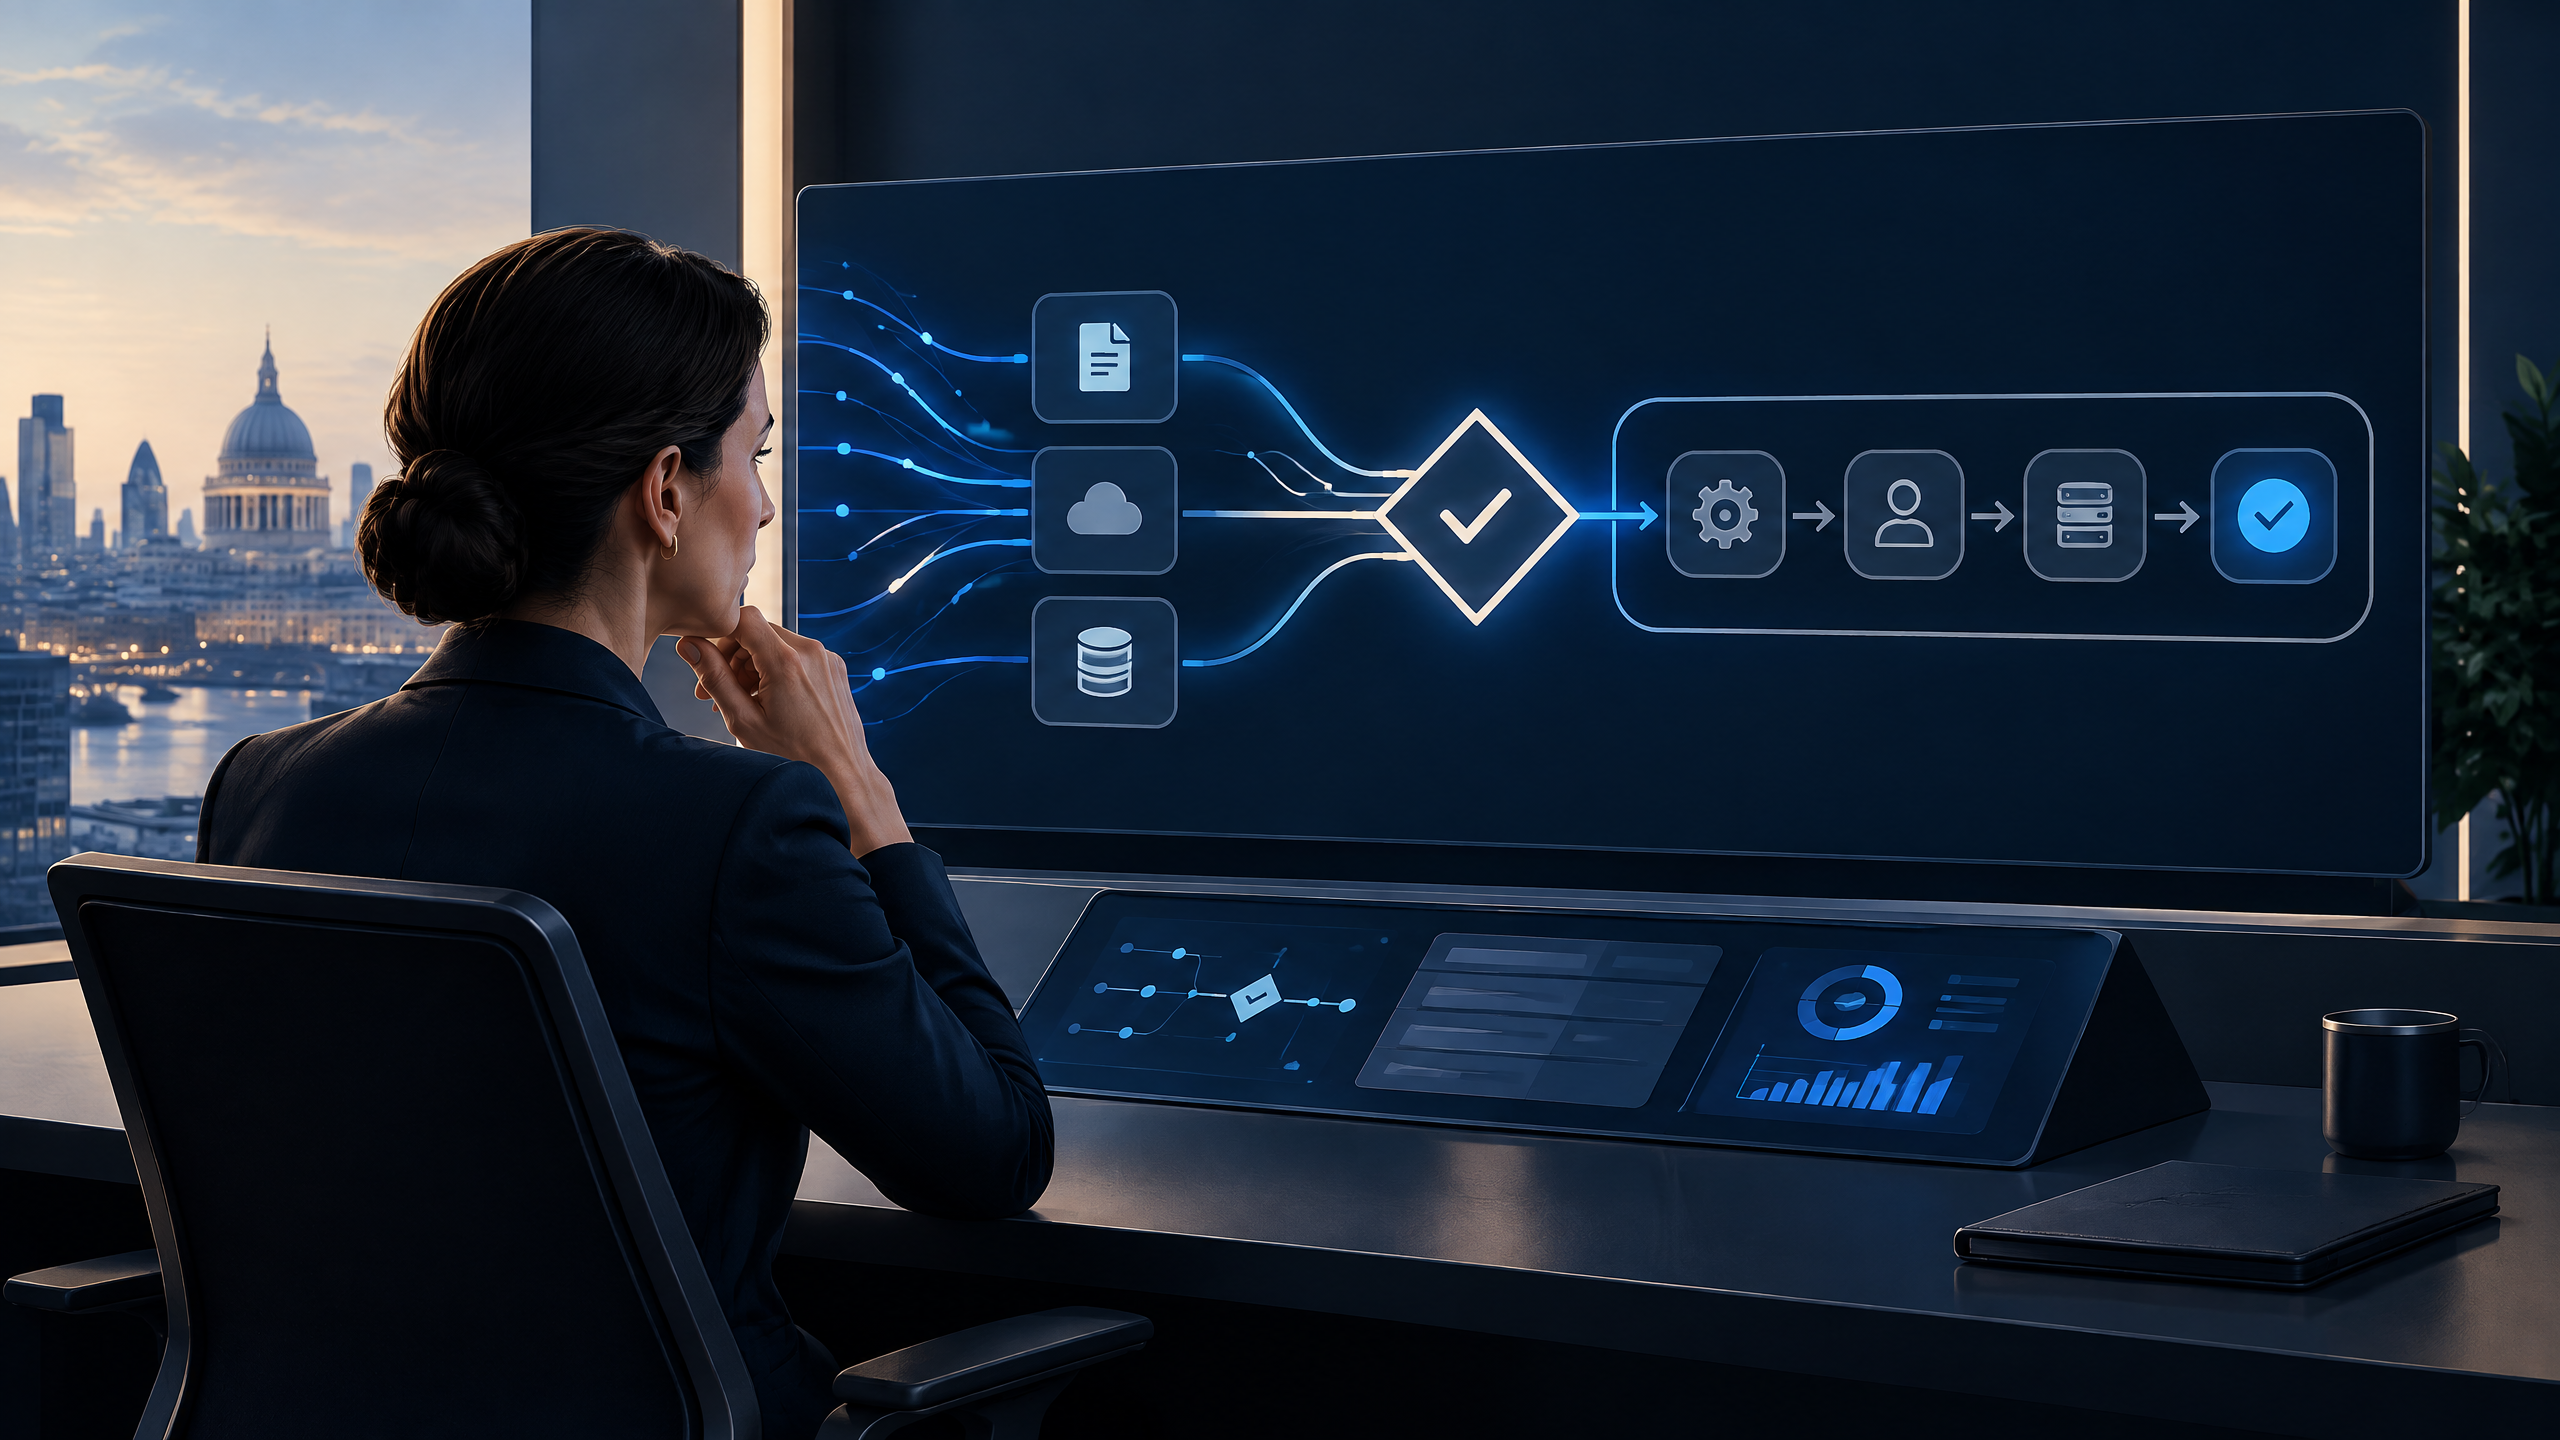
Most operational teams do not need an agent that can ‘run the business’. They need a way to remove repetitive coordination without quietly delegating judgement. That distinction becomes acute when an inbox triage agent can draft a reply, a sales agent can update a CRM, or a finance workflow can prepare an exception for approval. AI Agents And Automation can move work between systems quickly, but a fluent response is not evidence that a proposed action is correct, fair or within commercial authority. NIST identifies confidently stated but erroneous content (‘confabulation’) and human over-reliance among the risks that must be managed in generative-AI systems 1.
The business problem is therefore not simply ‘where can we automate?’. It is: which parts of a decision are repeatable operations, which require evidence, and which require an accountable person to exercise judgement? A governed agent workflow answers that question before it is connected to a live inbox, database or payment process.
The costly gap between a task and a decision
A task has an observable completion condition: retrieve a record, classify an enquiry, check a field, create a draft, assemble a report or route a case. A decision commits the organisation: accept a contractual term, make an employment choice, authorise a refund above a threshold, change a customer’s entitlement or publish advice that a client could rely on. One workflow can contain both, but they should not receive the same degree of autonomy.
This distinction is often obscured by a demo. An agent may appear to ‘resolve’ a customer issue because it has located an order and selected words that sound plausible. In production, the same interaction may require an accurate account history, a current policy, an exception check, a named owner and a record of what was approved. If any of those are absent, a fast response simply moves risk downstream.
A useful design principle is to automate information handling and bounded execution, not accountability. That can include extracting data from approved sources, matching it to a known record, drafting a response from a current knowledge base, scheduling a follow-up, or applying a pre-approved rule. It should not imply that the model has authority to invent policy, reinterpret a contract or settle a material exception. The UK Government’s AI Playbook similarly treats meaningful human control, accountable risk ownership and regular review as core elements of safe AI use 4.
AI Agents And Automation need two distinct boundaries
The first boundary is knowledge. An agent should know where its answers may come from: approved knowledge articles, product data, CRM fields, a governed ETL pipeline or named documents. It should expose the source or mark uncertainty instead of filling gaps with a persuasive guess. That does not make every output correct; it reduces the scope for unsupported answers and gives a reviewer something concrete to check.
The second boundary is authority. The workflow must specify what an agent may read, write, propose and trigger. A sensible rule is to make permissions narrower than the agent’s apparent capability. For example, an account-support agent might read order status, draft a customer reply and create a ticket, while being unable to issue a discretionary credit. A human service lead receives the exception, sees the evidence and makes the credit decision.
This is not merely a prompt-writing exercise. The NCSC advises organisations to define both intended scope and ‘red lines’, apply controls in addition to prompts, and set oversight in proportion to autonomy and potential impact 3. Its guidance also recommends unique, limited agent credentials and a sandbox that restricts access to only the resources needed for the task 3. In practice, that means allowlisted tools, role-based service accounts, thresholds in the workflow engine and an approval gate that cannot be bypassed by a well-worded model response.
Put human review at the commitment point
‘Human in the loop’ is too vague to be a control on its own. A reviewer who sees a queue only after an action has been sent is observing, not deciding. A reviewer who is expected to approve hundreds of near-identical recommendations in minutes may also be unable to challenge them meaningfully. The ICO says meaningful review requires people with appropriate knowledge, experience, authority and independence to challenge decisions; it also recommends logging overrides and the reasons for them 2.
Place the human decision at the irreversible or consequential commitment point, rather than forcing manual checks into every low-risk step. This preserves operational speed while concentrating attention where it can change an outcome. A practical decision sequence is:
- Frame the outcome. Define the business result, the users affected and the action that would count as a commitment.
- Separate the work. List data collection, validation, recommendation, execution and approval as different steps; do not label the whole chain ‘automation’.
- Set the authority matrix. For each action, state whether the agent may read, draft, execute a pre-approved rule, or only recommend. Name the human owner for exceptions.
- Define evidence and stop conditions. Specify approved sources, minimum fields, confidence or validation checks, monetary or risk thresholds, and the conditions that force escalation.
- Make approval usable. Give the reviewer the relevant record, source links, proposed action, policy rule and alternatives—not just an ‘approve’ button.
- Log, sample and improve. Retain the request, retrieved evidence, action, reviewer outcome and override reason. Sample low-risk decisions and revisit rules when exceptions cluster.
The sequence is deliberately bounded. It does not claim that a threshold or a reviewer removes all error. Its purpose is to make the organisation’s tolerance, ownership and route out of automation visible before scale makes a weak assumption expensive.
Build the control into the webstack and data flow
A governed agent is usually a workflow, not a single chat interface. The webstack supplies the entry points—forms, inboxes, CRM and reporting—while ETL processes normalise and validate the operational data that the agent is allowed to use. An orchestration layer then calls approved tools, applies deterministic rules and records the result. The human workbench handles review, exception resolution and feedback.
Consider an inbound business-development enquiry. The agent can extract company details from the form, de-duplicate against the CRM, classify the stated need, retrieve approved case material and create a suggested follow-up. A deterministic rule may assign the record to the relevant owner. Yet commercial fit, pricing, commitments and claims remain for a person who can weigh context that does not exist as a clean field. This is a more dependable use of an agent than giving it unrestricted CRM write access and asking it to ‘qualify leads’.
The same pattern applies to reporting. An agent can assemble weekly operational signals from a controlled data set and flag anomalies. A manager decides whether the movement is meaningful, what explanation is credible and what intervention is appropriate. Data lineage matters here: the ICO recommends mapping information flows across the supply chain and maintaining records of processing activities, while its governance guidance calls for documented change management and risk-based audit 5. Those disciplines make it easier to find out why an agent saw a particular value, which version of a rule applied and who changed it.
Measure whether the hand-off works
A deployment should be judged on more than volume processed. Track the rate of escalations, approval reversals, policy exceptions, unsupported-answer reports, time to resolution, and the quality of the evidence presented to reviewers. Segment results by workflow and risk tier. A low escalation rate may signal a well-bounded process, but it can also mean staff are not being shown uncertainty; review a sample rather than treating the metric as proof.
Start in a reversible, low-consequence workflow with a clear owner. Test representative and awkward cases, including missing data, conflicting records, ambiguous requests and attempts to push the agent outside scope. NIST’s profile calls for post-deployment monitoring, feedback, incident response, change management and escalation by people able to evaluate reported issues 1. The NCSC also advises maintaining a way to halt autonomous activity quickly if an incident occurs 3.
That operational discipline turns an agent from a promising interface into a controlled business capability. It creates a learning loop: exceptions improve source material, recurring approvals reveal rules that could be formalised, and repeated uncertainty identifies decisions that should stay human.
The practical objective: faster work, retained accountability
The strongest use of AI agents is not to imitate a senior operator. It is to give that operator better-prepared work, clear evidence and fewer routine hand-offs. The organisation retains responsibility for decisions; the agent works inside a deliberately limited operating space. How much autonomy is appropriate will always depend on the workflow, source quality, data sensitivity, ownership and controls in place.
If you are mapping a prospective agent workflow, see how Neuro-Performance AI approaches the process. For a measured discussion of decision boundaries, data flows and an appropriate first use case, request an architecture audit.
Sources
Sources
- [1]Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile — National Institute of Standards and Technology
- [2]Human review — Information Commissioner's Office
- [3]Managing the cyber risk of agentic AI — National Cyber Security Centre
- [4]Artificial Intelligence Playbook for the UK Government — Government Digital Service
- [5]Governance and accountability in AI — Information Commissioner's Office
Next step
Request an architecture audit
A free 30-minute review of where AI agents and a connected webstack could remove work from your business — checked by our MBA and PhD experts.
Request an architecture audit