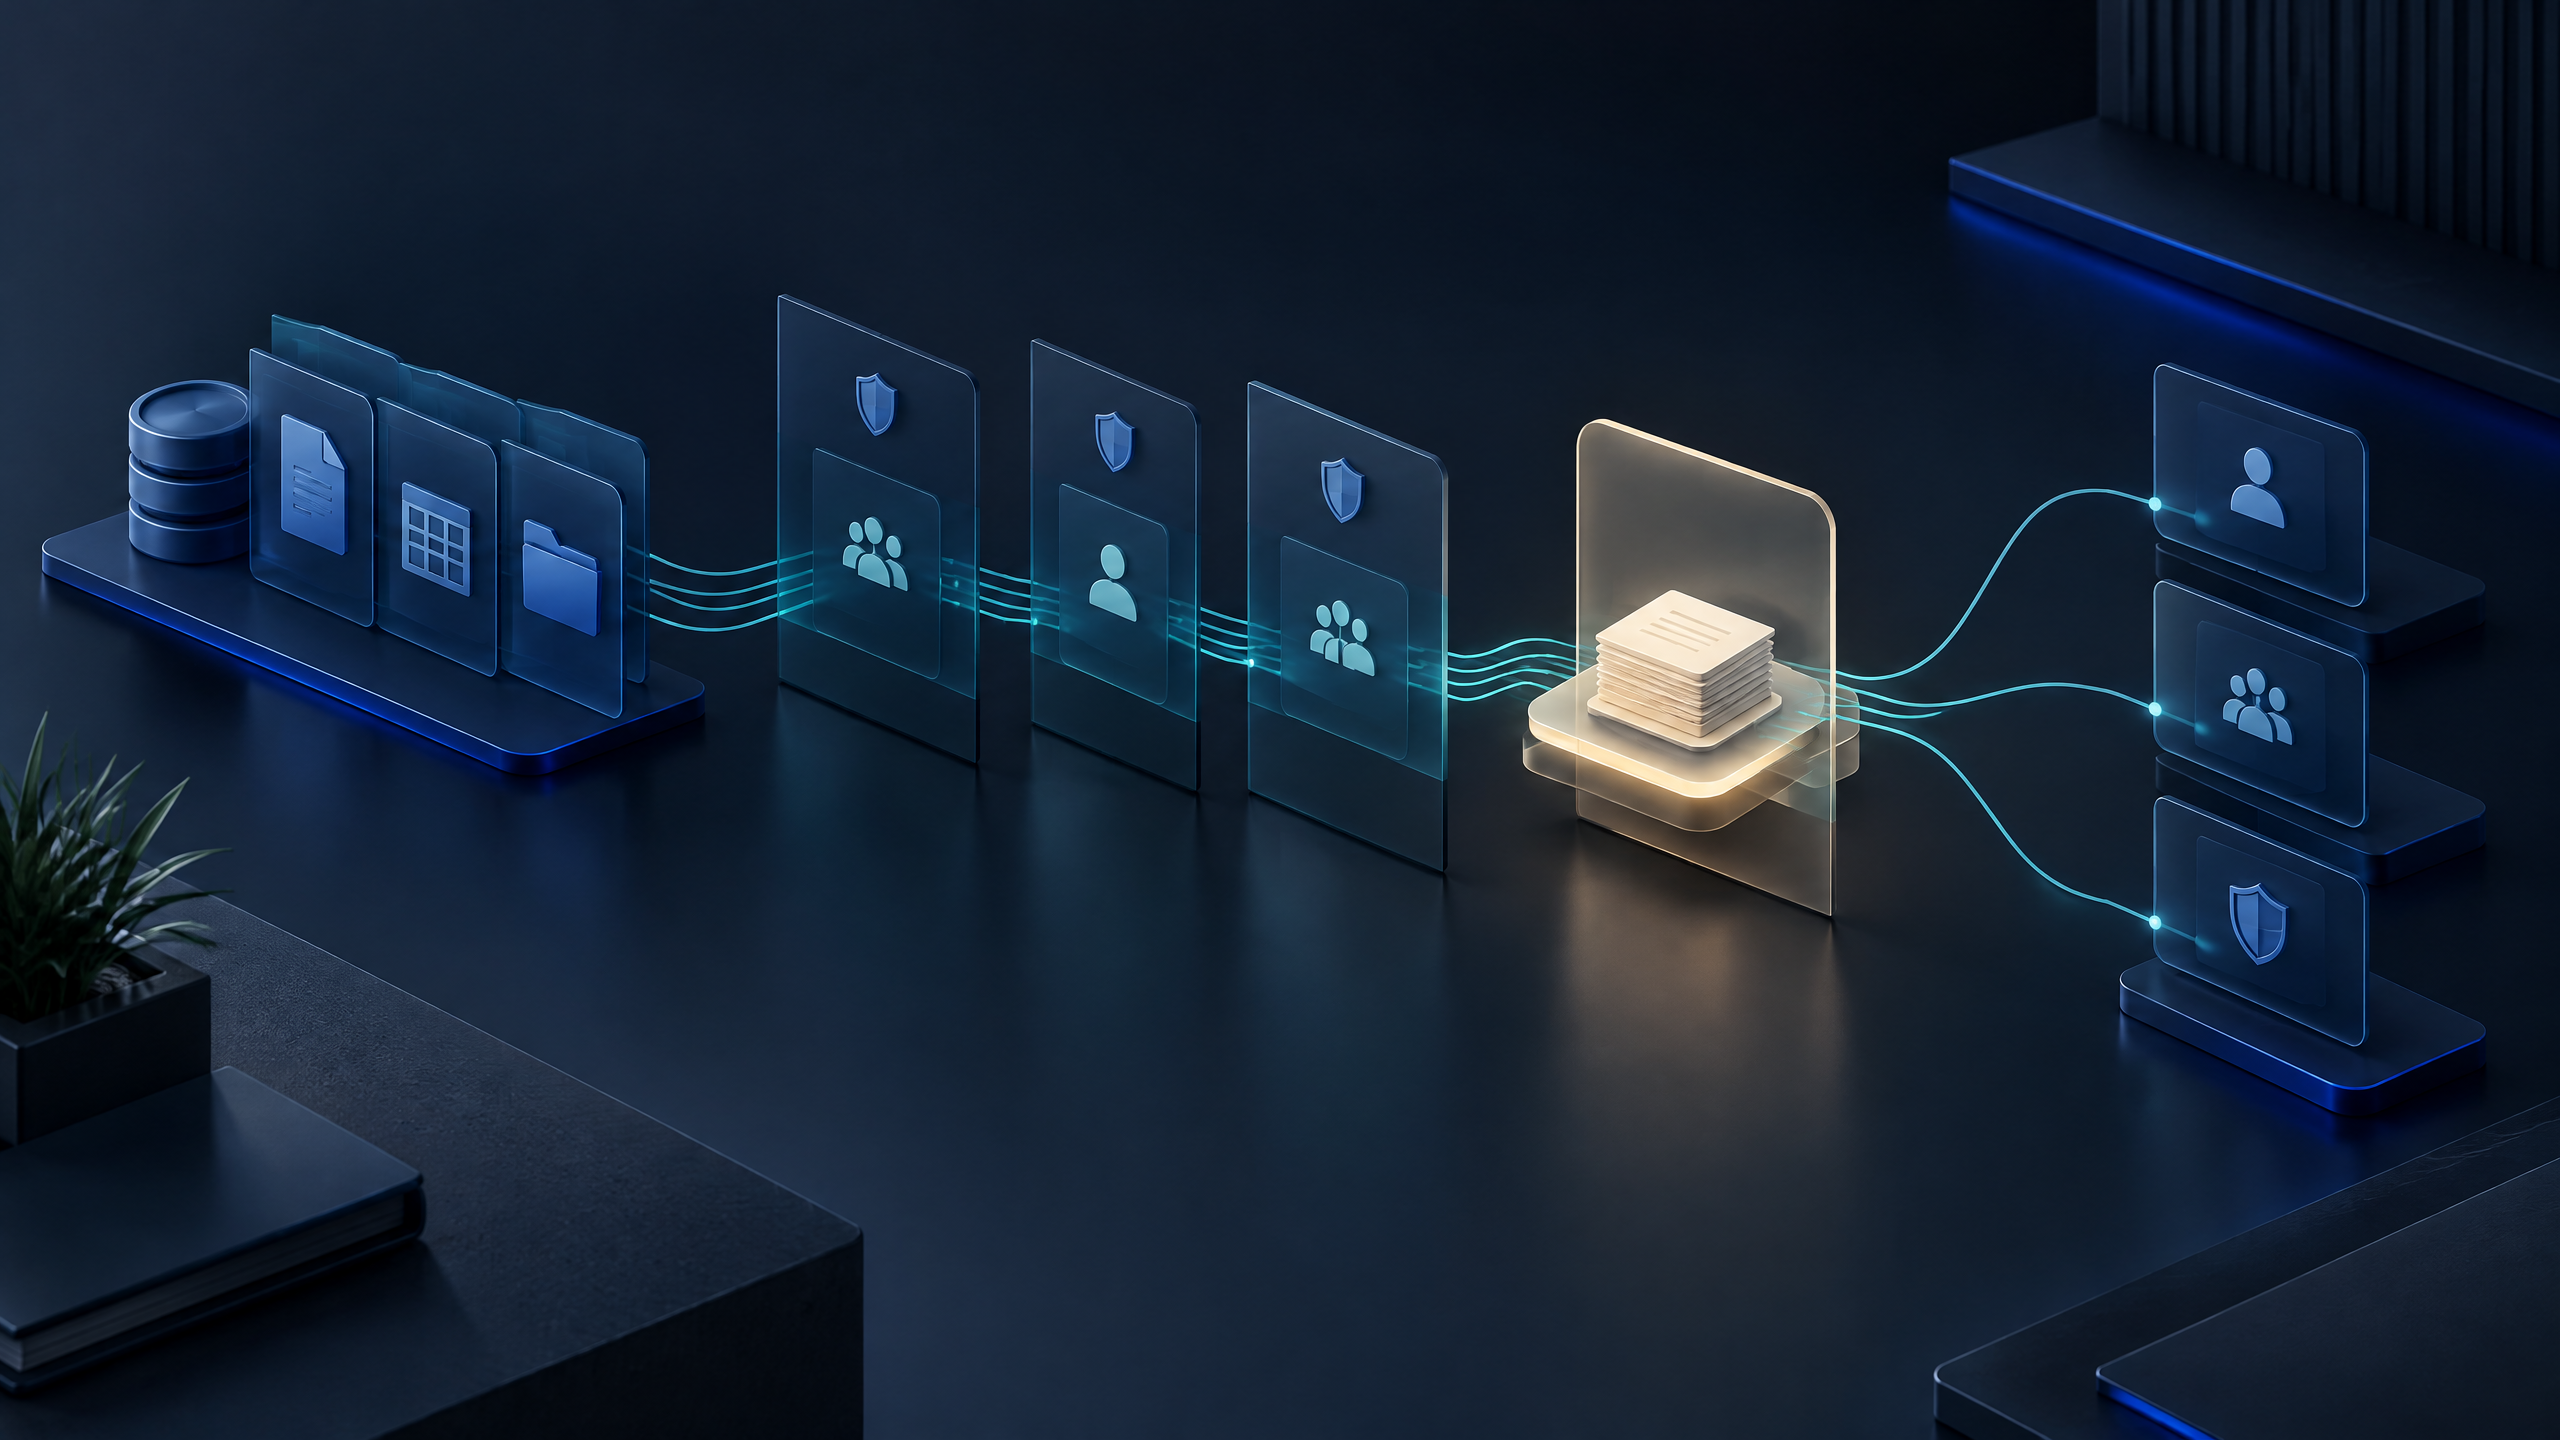
A founder searching for a private AI agent development company UK rarely begins with the technology. The immediate issue is concrete: a shared inbox contains sensitive requests, a consulting team repeatedly prepares briefs from client material, or operations staff move information between systems. The work is repetitive, but the information is too important for an unbounded tool.
The buyer must ask whether the workflow has enforceable boundaries: what information may enter, how it may be used, who can access it, what the agent may do and who remains accountable for a decision or commitment.
A governed implementation starts there. It makes the data route, permissions, model-service terms, tool permissions, records and review points visible before a live connection is made. That is more demanding than demonstrating a chat interface, but it gives a leadership team something meaningful to assess.
What a private AI agent development company UK should define first
“Private” is not one technical feature. It is a set of workflow-specific design and operating decisions, expressed as an answerable boundary schedule rather than a blanket assurance.
First, name the business purpose in one sentence. “Classify supplier requests and prepare a draft routing note” is testable; “help operations with procurement” is not. Map the minimum fields, documents and records needed. The ICO says data protection by default limits use of personal information to what is necessary for each specific purpose, including amount, processing, storage and accessibility. 1
That mapping changes the build. A routing agent may need the request text, supplier category and region, but not an entire historical mailbox. A draft engagement summary may need a defined project folder and template, not open access to every client workspace. Where the workflow permits it, a delivery design can exclude fields, reduce detail or apply pseudonymisation before material reaches the model. These are purposeful controls, not promises that a system is universally safe or compliant.
Second, separate where data travels from who can act on it. Identify each hand-off—source, preparation, model service, review queue and destination—along with environments, credentials, retention and ownership. The UK AI Cyber Security Code calls for documented requirements, risks and mitigations, plus an audit trail for models, datasets and prompts. 3 Ask whether a supplier can explain that route without a diagram labelled simply “AI”.
Finally, verify the actual service terms, account configuration and contract documents for the selected provider and product—not a general claim about “public models”. A buyer needs to check the exact offering, current terms, data-processing arrangements and configuration proposed for its own processing. That is not a shortcut to a privacy or compliance conclusion; it is part of understanding what has actually been designed.
Design the data boundary before the integration
Do not connect a broad source and work out the rules later. Begin with a small job and a data contract that business, technical and delivery owners can all read.
Take a non-identifying example. A UK professional-services firm wants quicker handling of prospective-client enquiries. Its agent may read messages submitted through a controlled form, extract agreed fields, check those fields against a published qualification policy and prepare a draft internal routing record. It does not search unrestricted client folders, make eligibility promises, send a proposal or amend the CRM without a defined approval. The human owner accepts, changes or rejects the recommendation at the commitment point.
For that workflow, the data contract should state:
- the approved sources and fields, including excluded categories;
- the permitted purpose and permitted outputs;
- the model-service and storage choices being evaluated;
- retention, deletion and access-review decisions;
- roles allowed to view the queue, approve an action or change a rule; and
- the event record required when the workflow is run, reviewed, escalated or changed.
This is a build input, not a policy exercise. The ICO recommends mapping the information, purpose, risks and measures, with role-based or named access controls and a process to grant or revoke access. 1 Where a planned use is likely to create high risk to people’s rights and freedoms, the ICO says a DPIA is required; obtain suitable specialist advice where needed. 1
A private workflow also needs a change boundary. Adding a new source, tool, user group, action or purpose is not a minor prompt edit. It should return to assessment, test and approval. This preserves the ability to say what the agent was authorised to do at a given time.
Turn the model into a constrained component, not a system owner
An agent becomes risky when reading text also grants broad authority. Uploaded files, webpages, emails and retrieved documents are relevant: OWASP describes indirect prompt injection as external content that changes LLM behaviour when processed, and says retrieval and fine-tuning do not fully remove it. 4
The architectural response is not to trust a cleverer prompt. It is to make the model one component within controls that do not depend solely on the model following instructions. For the professional-services example, that means treating a submitted message as untrusted content, separating it from the agent’s governing instructions and passing any proposed CRM update through deterministic validation. The model can return a defined schema—such as category, confidence rationale and proposed owner—but application code checks allowed values and the target system performs the update only after the relevant approval.
Tool permissions deserve the same care as data access. Give each workflow a dedicated identity with the smallest useful scope, rather than handing the model a staff member’s general credentials. Constrain operations to the named record or queue where possible. Do not expose a generic “send email”, “download files” or “search all drives” capability if the job only needs to create a draft record. The NCSC advises restricting possible actions where AI components trigger actions, using least privilege and applying suitable controls to data sent to external services. 2 The UK Code similarly calls for access-control measures that secure APIs, models, data and processing pipelines, and for separation of environments. 3
Human review belongs at a defined control point: a duty manager approves outbound communication, a partner checks a summary or an operations lead resolves a missing category. The screen should show source evidence, proposed action and a reject or escalation route. The UK Code recommends human-oversight capabilities and outputs that responsible people can assess. 3
Test the boundary, not just the happy path
A polished demonstration proves that a system can produce a plausible answer. It does not prove that the surrounding controls behave properly when inputs are messy, access changes or content tries to redirect the workflow.
Before a limited release, test with realistic but safe cases: incomplete requests, contradictory documents, unexpected file formats, prohibited categories, revoked permissions, requests outside the agreed purpose and attempted prompt injections. Verify that the workflow withholds an action, routes to a person or creates an auditable exception as designed. OWASP recommends least privilege, human approval for high-risk actions, segregation of external content and regular adversarial testing as ways to reduce the impact of prompt injection. 4
Monitoring should answer: which source, rule and prompt version applied; which service and tool ran; what was proposed; who approved or overrode it; and what failed. The NCSC recommends threat modelling for unexpected behaviour, access controls across APIs, models and data, incident procedures and high-quality audit logs. 2
This record supports measured improvement. A review can identify a recurring exception, correct an approved source, narrow a tool permission or decide that the task belongs with a person. It does not turn the agent into an authority. The accountable owner remains responsible for deciding whether the scope, controls and evidence are sufficient for continued use.
A bounded buying conversation
The right first deliverable from a private AI agent development company is not an all-access connection. It is a scoped architecture: one workflow, one outcome, named data categories, a source-to-action route, access roles, model-service questions, test cases, escalation path and decision owner. That artefact lets a founder compare suppliers on the mechanism of delivery rather than on an unqualified claim of privacy.
Neuro-Performance AI can help leaders turn a real operational bottleneck into that governed scope, drawing on structured review, approved-source design and defined human decision points. See how the delivery process works, then request an architecture audit for a focused conversation about one workflow. The next step should be small enough to test, clear enough to govern and useful enough to justify connecting any business data.
Sources
Related insights
- AI Agents for Business: Where They Create Useful Work—and Where They Should Stop
- Knowledge Based Agent in Artificial Intelligence: Turning Approved Information Into a Useful Business Guide
- AI Agent Types: A Practical Way to Choose the Right Operating Model
Sources
Next step
Request an architecture audit
A free 30-minute review of where AI agents and a connected webstack could remove work from your business — checked by our MBA and PhD experts.
Request an architecture audit