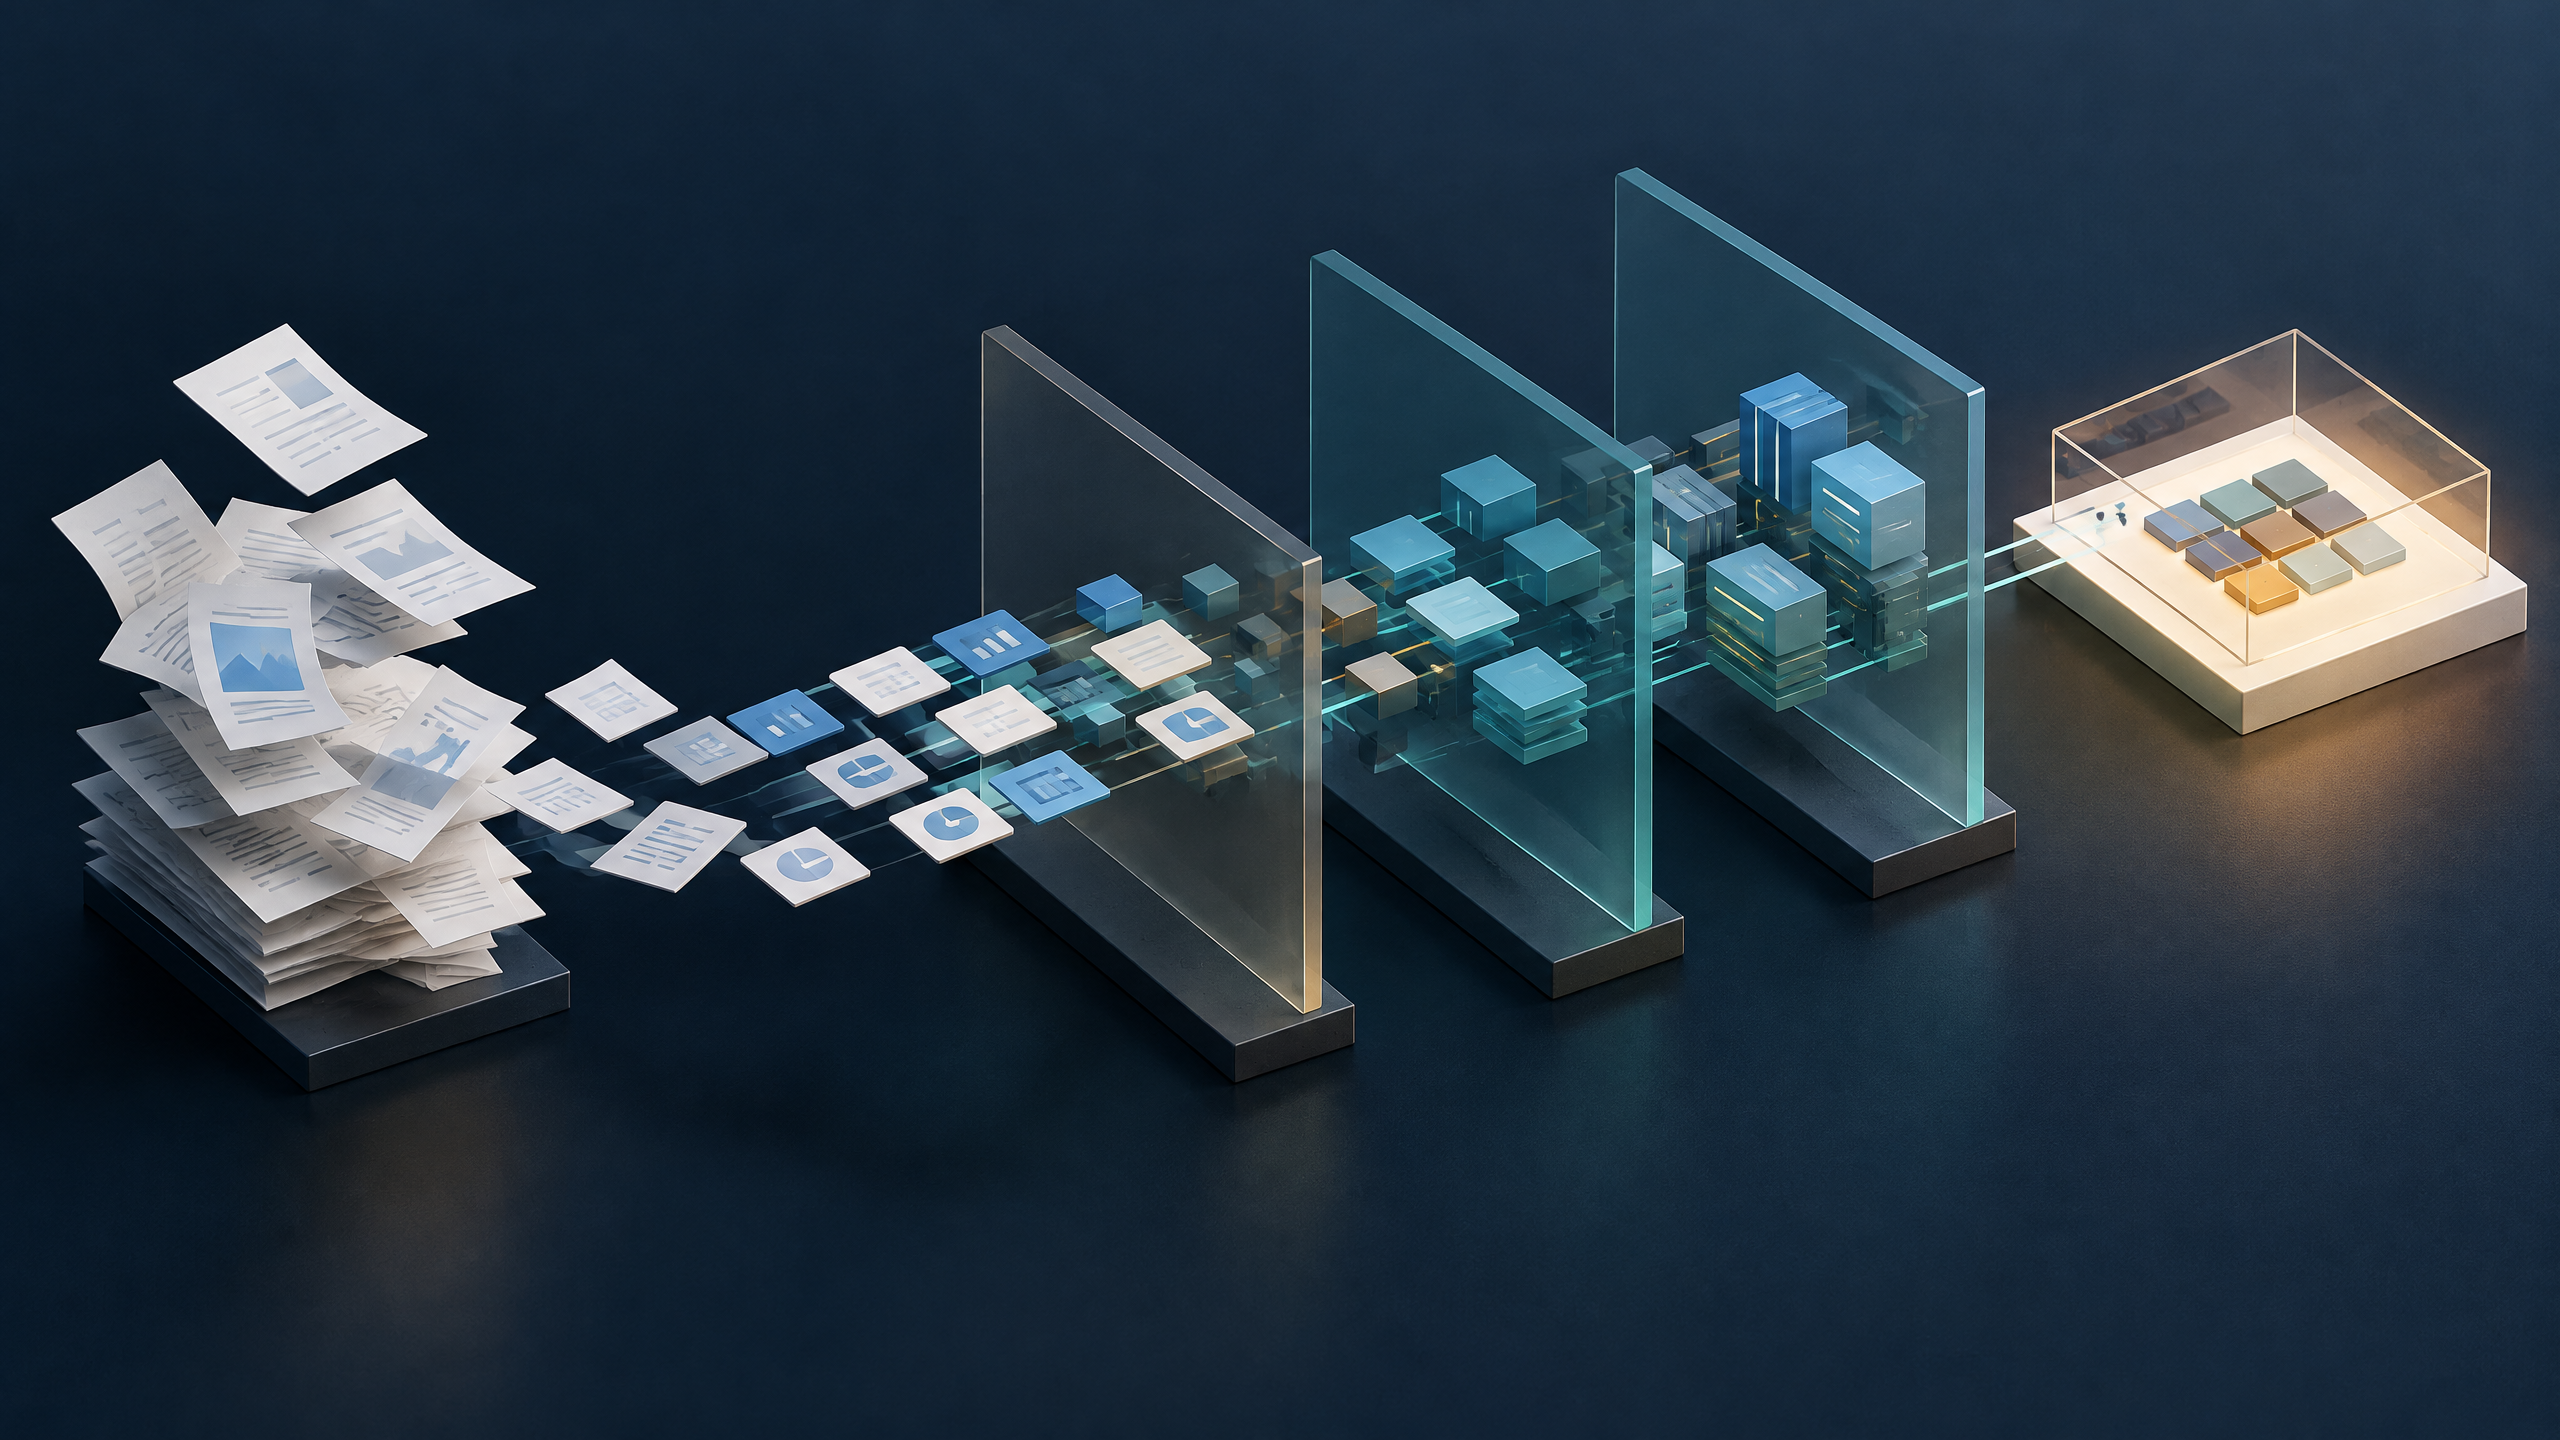
Teams rarely look for AI data processing automation services UK because they want a more impressive workflow diagram. They look because capable people are still opening attachments, copying facts into line-of-business systems, normalising inconsistent fields and chasing the records that do not match. The visible cost is time. The harder problem is that each manual hand-off hides a choice: which source is authoritative, what happens when a value is missing, and who is allowed to turn a proposed record into a committed one.
A useful implementation does not hand those choices to a model. It makes the repetitive preparation work machine-assisted while keeping data standards, exceptions and consequential actions inside an explicit operating design. That is the difference between a fast demo and a workflow an operations leader can inspect, pause and improve.
AI data processing automation services UK should start with a bounded unit of work
The first decision is not which model to use. It is which narrow operational unit can be stated clearly enough to test. “Process incoming supplier documents” is too broad. “Read a defined set of fields from approved invoice PDFs, compare them with a purchase-order feed, then create a review item where required fields or matching rules fail” is a workable boundary.
That statement becomes a short operating contract. It identifies the permitted input locations, the data fields that are in scope, the target schema, the rules that decide whether a record may move forward, the owner of an exception queue and the actions the workflow is forbidden to take. It should also distinguish a proposed value from a value already confirmed in the system of record.
This matters especially where personal data appears in the work. The ICO says data minimisation means personal data should be adequate, relevant and limited to what is necessary for the stated purpose; it also says organisations should be able to demonstrate appropriate processes for this. 2 In practical terms, a design can pass only the fields required for the specified task, rather than presenting a whole mailbox, customer record or document repository by default. Whether and how UK data-protection obligations apply is a question for the organisation and appropriate advisers, not something an automation supplier can certify from a generic brief.
A bounded workflow is also easier to compare with the established delivery approach set out in how the delivery process works. The commercial question becomes concrete: which manual checks can be made more consistent or faster, while leaving the accountable decision in the right hands?
Build a chain of controls, not one confidence score
Trustworthiness is not supplied by a percentage beside a model output. It arises from several controls that work together. The NIST AI RMF Playbook organises suggested actions around Govern, Map, Measure and Manage, including topics such as context of use, data, documentation, testing, human oversight, monitoring and incident response. It is voluntary rather than a universal checklist, but it is a useful structure for discussing an implementation. 1
For a data-processing workflow, the chain normally starts with an input contract. Define the approved source, expected file or record type, allowed fields and version rules. A workflow should reject or quarantine inputs outside that contract rather than attempting to infer a new business process from them.
Next comes validation before write-back. A model may help extract or classify unstructured material, but deterministic checks can test formats, required fields, permitted codes, duplicates and reconciliations against a defined source. The workflow can attach its proposed values, source reference and validation outcome to a review item. It should not silently overwrite a record merely because a response appears plausible.
Then define exception and authority paths. Low-risk, fully validated records may be eligible for a predefined onward step. Records with missing evidence, conflicts, unusual values or a change to an external commitment should go to a named queue. A person with the relevant operational authority decides the commitment point. This is not a claim that human review removes every error; it is a way to expose uncertainty where it matters.
Finally, make the process observable. The NCSC describes logging as a retrospective audit trail and monitoring as ongoing observation; its API guidance recommends recording access, error and transaction activity while avoiding sensitive data such as passwords, keys, tokens and personally identifiable information in logs. 4 A proportionate implementation can therefore record the workflow version, input reference, validation results, exception route, reviewer decision and output reference, while designing logs to avoid unnecessary sensitive content. Those records make a failed or disputed item traceable without treating a chat transcript as the system of record.
Design for correction, replay and a clear system of record
The operational risk is not only that a value is extracted incorrectly. It is that a wrong value spreads across systems with no practical route back. The design should name one system of record, preserve the source reference for each proposed record and separate raw intake, normalised data and approved output. That makes it possible to locate a record, correct it at the right stage and replay a defined batch after a rule or mapping changes.
This is a control for operational reliability, not a promise of perfect data. The ICO’s accuracy guidance says organisations should take reasonable steps to ensure the accuracy of personal data, make the source and status clear, and correct or erase inaccurate or misleading information without delay where required. It also notes that the appropriate effort depends on the nature and intended use of the data. 3 For a buyer, that supports a practical question at discovery: what must be retained to explain a value’s origin, and who can correct a record when a source is wrong?
Consider a UK professional-services firm receiving client onboarding packs by email. A governed workflow might collect documents from a defined inbox, extract a limited registration-data set, check mandatory identifiers against a supplied schema and create a draft record in an internal review queue. It can flag a missing field, duplicate or contradictory address for the operations team. It does not decide whether to accept a client, change contractual terms or make an external commitment. Once a reviewer approves the draft, an authorised integration can write the confirmed record to the chosen business system.
The point is not to automate every step. It is to remove repetitive preparation from the path, retain a visible exception route and avoid building a shadow database that staff cannot reconcile.
Test the failure paths before asking staff to depend on it
A credible pilot includes awkward cases, not just clean examples. Test unreadable documents, changed templates, duplicate submissions, conflicting system records, absent mandatory values, unusual volumes and a failed downstream connection. For each case, define the expected outcome: rejection, quarantine, retry, review or stop. Test whether the workflow avoids an unauthorised write when that outcome occurs.
The UK government describes AI assurance as measuring, evaluating and communicating the trustworthiness of AI systems, and frames it as part of wider organisational risk management. 5 In a data-operations context, assurance can be kept practical: maintain a sample set of representative cases, test changes against it, record the outcome, review live exceptions and retain an owner for changes to mappings, prompts and access permissions. The aim is evidence for a bounded use case, not a blanket declaration that an AI system is compliant or reliable in every context.
Monitoring should also trigger a business conversation, not only a technical alert. A rising proportion of exceptions may mean an upstream form changed, an input source has degraded or the scope now needs redesign. The right response may be to pause a route, update a rule or return work to a human queue while it is investigated.
Move from a bottleneck to a scoped architecture
Before selecting a provider, map one real workflow from intake to committed outcome. Bring two or three typical inputs, the target data fields, known exception categories, every system touched and the person who owns the decision at each hand-off. This makes it possible to assess the integration, data boundaries, review experience and audit evidence needed for that workflow rather than buying a generic “AI automation” package.
Neuro-Performance AI can use that material to frame a scoped architecture conversation: what should be automated, what should be validated, what should be reviewed and what must remain outside the workflow’s authority. For a measured next step, request an architecture audit focused on one data-processing bottleneck and its controls.
Sources
Related insights
- ETL Pipelines: The Invisible Foundation of Reliable Automation
- AI Agents and Automation: How to Keep the Human Decision Where It Belongs
- Private AI Agent Development Company UK: Designing Boundaries Before You Connect Business Data
Sources
- [1]NIST AI RMF Playbook — National Institute of Standards and Technology
- [2]Principle (c): Data minimisation — Information Commissioner’s Office
- [3]Principle (d): Accuracy — Information Commissioner’s Office
- [4]Securing HTTP-based APIs: Logging and monitoring — National Cyber Security Centre
- [5]Introduction to AI assurance — GOV.UK
Next step
Request an architecture audit
A free 30-minute review of where AI agents and a connected webstack could remove work from your business — checked by our MBA and PhD experts.
Request an architecture audit