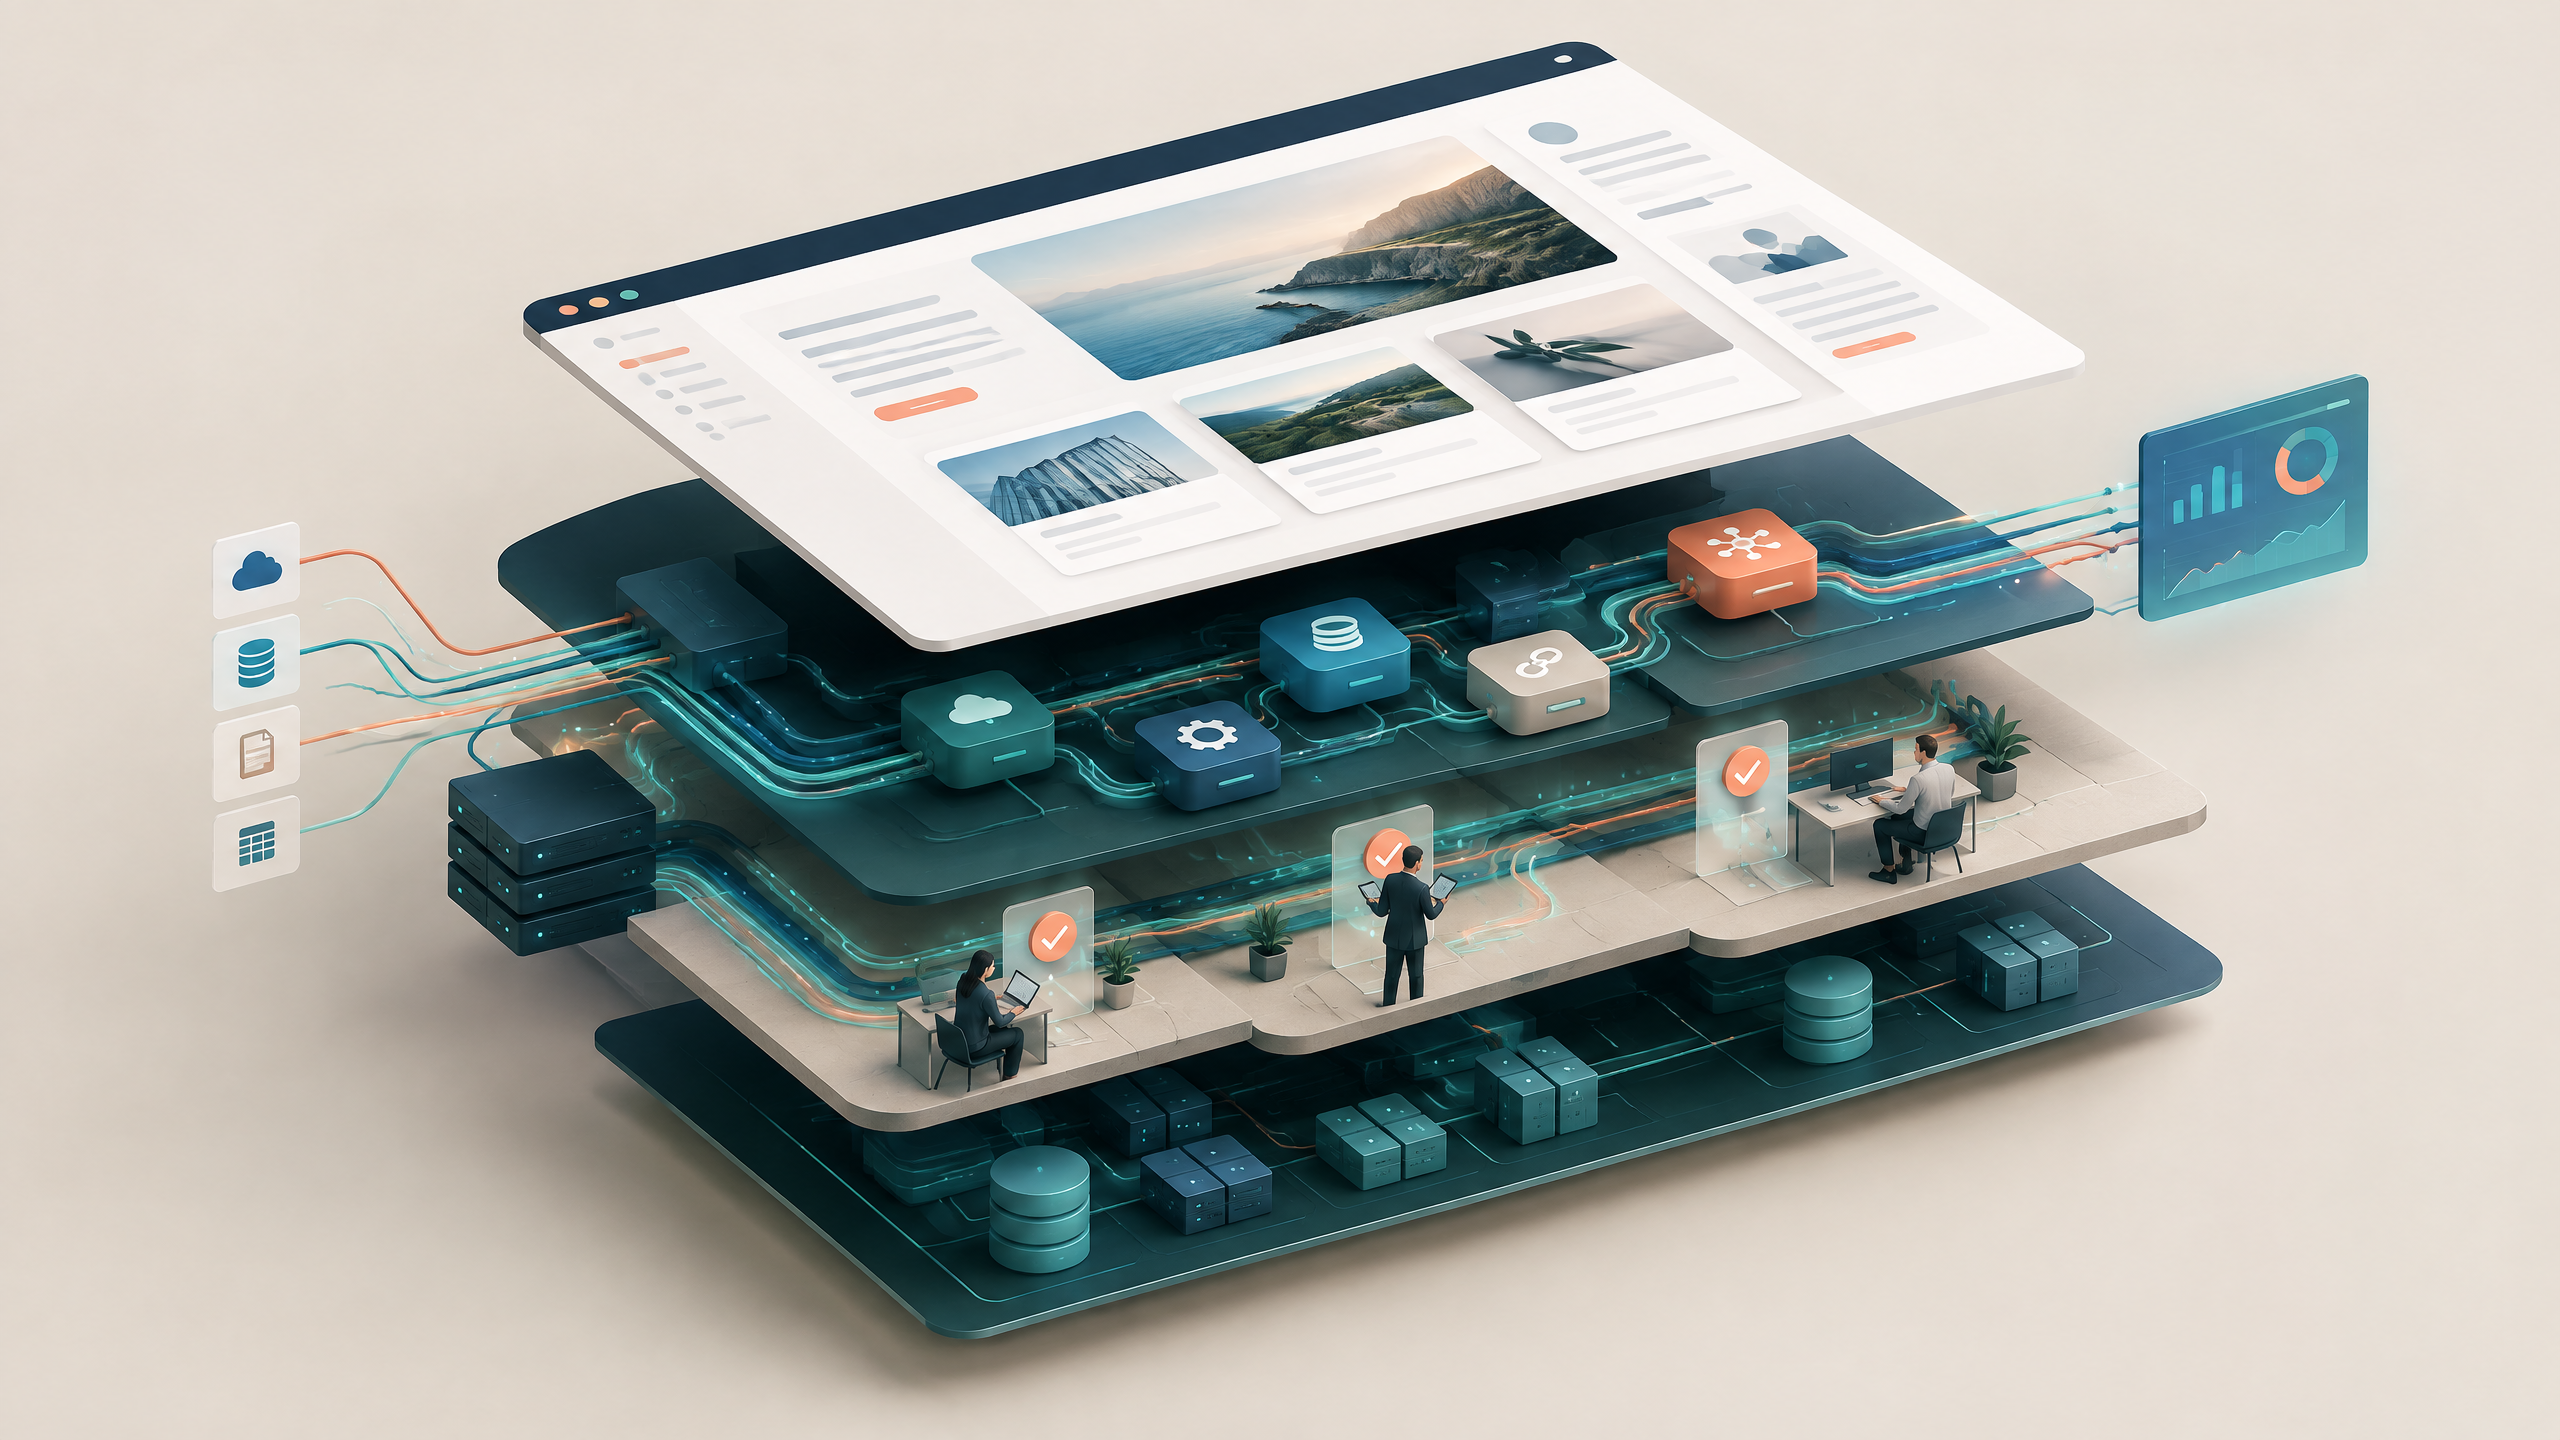
A company website is often treated as a polished endpoint: pages, forms, case studies and a booking link. That view is too narrow. Webstacks are the operating layer behind the visible site: the connected content, data, measurement, routing, security and human-review practices that let the site do useful work after a visitor arrives. For a growing professional-services firm, the commercial problem is rarely a lack of pages. It is the gap between attention, a useful next step, and reliable follow-through.
A beautiful site can still lose intent when a prospect cannot find the relevant proof, a form sends an incomplete enquiry into an unowned inbox, a webinar registration never reaches the CRM, or leaders see only traffic rather than decision-ready evidence. Adding an AI assistant to that fragmented environment can make the gaps more visible, but it does not repair them. The better question is: what operating system must sit behind this website so that each interaction has a purpose, an owner and an appropriate control?
Webstacks turn a website into a managed business system
A webstack is not one product or a fashionable replacement for a website. It is a deliberately connected set of capabilities that moves a visitor from discovery to a suitable next action while preserving the context needed by people and systems downstream. Its components normally include:
- an audience and proposition model, reflected in content and landing pages;
- a content and experience layer, including accessibility and performance quality;
- capture and routing, such as forms, scheduling, consent choices and CRM records;
- an integration and data layer that validates, transforms and synchronises events; and
- measurement, governance and improvement routines.
Business outcomes sit across hand-offs. A visitor asking about a leadership programme may need a clear explanation, accessible navigation, a low-friction way to enquire, acknowledgement of what happens next, and a correctly routed record for the right person. A website that fulfils only the first two tasks is a brochure, not an operating system.
The model also changes the build conversation. Instead of asking which widgets to add, a founder can specify a service hypothesis: if a prospective client sees relevant evidence and can state their situation in a short, usable form, then the right adviser can respond with enough context to decide the next step. GOV.UK’s service-measurement guidance recommends defining purpose, deriving benefits, testing hypotheses and choosing metrics that explain whether the service is working. It also advises combining quantitative data with user research rather than relying on analytics alone.1
The mechanism: connected journeys, clean events and clear ownership
A working webstack has to make three mechanisms explicit.
First, design the journey as a sequence of decisions. Define the priority audiences, their questions, the evidence they need, the legitimate next action and the accountable owner. A first-time visitor, a referred prospect and an existing client should not automatically be sent through the same path. This does not mean multiplying pages indefinitely; it means deciding which content, prompt or route earns its place.
Second, treat web data as operational input, not a trail of disconnected tags. A useful event model gives a stable name and meaning to events such as a resource request, an enquiry, a meeting booked or a qualified hand-off. An ETL-style layer can extract events from the site and connected tools, validate required fields, standardise values such as service interest or campaign source, and load approved records into reporting or workflow systems. Where data quality fails—for example, a missing consent state, malformed email address or unmapped campaign—the record should be held, flagged or routed for review rather than quietly presented as complete.
This is the unglamorous work that supports trustworthy reporting. It allows a commercial leader to ask not only “how many visits?” but “which approved journey produced a conversation, with which audience, and did our follow-up meet the agreed service level?” Metrics should be defined before implementation, viewed over time and segmented where it changes the interpretation. GOV.UK specifically notes that device type and new-versus-returning users can make an overall average misleading, and that data should help teams understand what happened, why, and what to do next.1
Third, assign ownership at every hand-off. The marketing lead may own a content hypothesis; operations may own lead routing; a partner may own the consultation decision; a data owner may approve fields and retention; and a technical owner may own releases, monitoring and rollback. A named owner makes a failed journey diagnosable. Without one, a conversion issue becomes a vague argument about “the website”.
Build experience quality and resilience into the operating layer
The visible experience remains important, but it should be designed as an operating concern. Web Content Accessibility Guidelines (WCAG) 2.2 provides technology-neutral, testable success criteria and is organised around content being perceivable, operable, understandable and robust.2 That is a practical prompt for a webstack: can a person complete the intended action with a keyboard, understand what a form requires, recover from an error and use the service on their device? Accessibility evaluation should involve appropriate testing and user evidence; a checklist alone does not prove that every person’s needs have been met.2
Performance needs the same discipline. Google describes Core Web Vitals as real-world measures of loading performance, interactivity and visual stability. Its published guidance suggests targets of 2.5 seconds for Largest Contentful Paint, under 200 milliseconds for Interaction to Next Paint and under 0.1 for Cumulative Layout Shift as user-experience objectives.3 They are useful guardrails, not a promise of search rank or commercial results. A founder should review them alongside completion, abandonment, accessibility findings and qualitative feedback—not chase a single score.
The system also needs resilience. The NCSC frames secure design around understanding all components, making compromise and disruption harder, making detection easier and reducing the impact when a compromise occurs.4 Applied to a website operating layer, that means documenting domains, forms, analytics, APIs, scripts, data destinations and privileged accounts; minimising what each connection can access; maintaining logs and alerts that someone reviews; and keeping a tested route to disable a failing integration. The exact control set depends on the risk, architecture and data involved.
Where governed AI agents belong—and where they do not
Governed AI agents can be valuable within a webstack when the task is bounded, the source material is approved and the consequence of error is manageable. Examples include drafting a response to a common enquiry for human approval, classifying a request into a pre-defined service area, identifying unanswered questions in site-search logs, or preparing a weekly content-performance summary from validated data.
The point is not to make the agent appear autonomous. It is to give it a specific role, defined inputs, permitted actions, output format, escalation route and review method. NIST’s AI Risk Management Framework is voluntary guidance designed to bring trustworthiness considerations into the design, development, use and evaluation of AI systems; its GenAI profile addresses risks specific to generative AI.5 A webstack can use that logic to maintain an agent register: purpose, data sources, access rights, refusal conditions, evaluation examples, accountable owner and change history.
For UK organisations processing personal data, the boundary matters further. The ICO’s AI and data-protection guidance addresses accountability and governance, transparency, lawfulness, accuracy and fairness across the lifecycle, and notes that the guidance is under review following changes in the Data (Use and Access) Act.6 This is not a reason to avoid useful automation. It is a reason to decide before deployment what personal data is necessary, what the lawful basis and retention approach are, who can access it, and when an agent must hand a case to a person. Agents should not make autonomous high-consequence decisions, give legal, financial or medical advice, or become an unreviewed front door to sensitive information.
A founder’s five-step webstack review
Use this short review before adding more campaigns, tooling or agents:
- Name the journey. Choose one high-value audience and define the evidence, action and owner for each stage from entry to follow-up.
- Draw the data path. List each field captured, each system it enters, transformations, consent or permission state, and the point at which a human can correct it.
- Set a small scorecard. Combine journey completion and response-time measures with qualitative feedback, accessibility checks and technical performance indicators. Establish a baseline before declaring improvement.1
- Set controls proportionately. Document integrations, access, change approval, monitoring, escalation and rollback. Apply the control depth to the risk, not a generic template.4
- Bound the agent. If AI is useful, start with a narrow assistive workflow using approved sources, a named owner and sampled review. Expand only when evidence supports it.
A webstack does not guarantee conversion, error-free automation or compliance. It exposes the assumptions between website activity and business follow-through so the team can test and improve them. Results depend on the proposition, source quality, traffic mix, workflow ownership, implementation and ongoing controls.
For founders who want to see how a small specialist team approaches the journey, data and governance layers together, review how the service works. If you are assessing an existing site or planning a new operating layer, request an architecture audit to start a measured conversation about the highest-value workflow to improve.
Sources
Sources
- [1]How to set performance metrics for your service — GOV.UK
- [2]Web Content Accessibility Guidelines (WCAG) 2.2 — W3C
- [3]Understanding Core Web Vitals and Google search results — Google Search Central
- [4]Secure design principles — National Cyber Security Centre
- [5]AI Risk Management Framework — National Institute of Standards and Technology
- [6]Guidance on AI and data protection — Information Commissioner’s Office
Next step
Request an architecture audit
A free 30-minute review of where AI agents and a connected webstack could remove work from your business — checked by our MBA and PhD experts.
Request an architecture audit